A practical GDPR review for your website chat
Start with three pieces of information: a public care guide, a customer’s message and an email left after closing. Each needs a different decision.
A florist uploads its public flower-care guide. Later a customer types a recipient’s home address into the chat. After closing, someone leaves an email for a callback. All three enter a support workflow, but only one was intended for publication. A meaningful privacy review starts by drawing those paths separately.
Walk through the chat as a visitor
Open a clean browser profile on your own storefront. Look at what loads before the widget is opened, what changes when you type and what is requested after hours. Record the services contacted and any browser storage you observe. A design review of the privacy page alone will miss differences introduced by your shop theme, tag manager or other plugins.
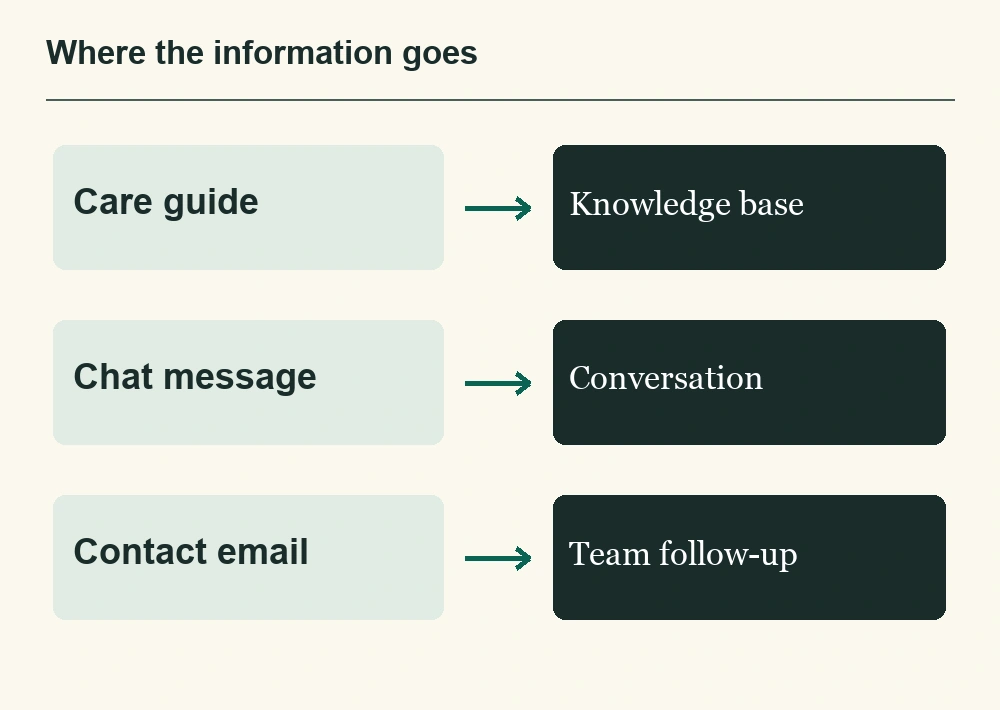
| What enters the service? | Why is it needed? | Question for the review |
|---|---|---|
| Public care instructions | Answer questions about flowers. | Is the source approved for use in visitor answers? |
| Chat text and possibly an address | Help with a specific enquiry. | Which colleagues and service providers receive it, and for how long? |
| Email left after closing | Respond to that person. | Is the purpose clear where the address is requested? |
Match the paperwork to the actual path
Identify the controller and processors for your deployment and the legal basis for each purpose. Check the information you provide under Article 13 GDPR. Where a provider processes data on your behalf, review the Article 28 terms, subprocessors and deletion arrangements. If processing involves transfers to third countries, assess the relevant transfer arrangements as well. An EU server location alone cannot settle those questions.
Legal text: Regulation (EU) 2016/679, Articles 5, 6, 13 and 28 and Chapter V.
Make the review useful at the counter
With QuatroChat you can start with public pages and free human chat. Add AI only to the sources you want used for customer answers. A policy from the website and a customer’s individual support record have different purposes. Keep private customer records out of material supplied as general knowledge. Ask a colleague to try the offline contact flow and explain in their own words what happens next.
Give one person responsibility for revisiting the inventory when you add a source, change providers or introduce a new field. A dated record of those choices is more useful to the next colleague than a “GDPR compliant” sticker.
Read our privacy information alongside your own data inventory